A bank alert is not a marketing message with a different label. It is a message the institution may have to prove it sent, to a customer who may have to rely on it, which is why the on-premise versus cloud question is decided on evidence rather than on cost per message.
This article sets out why alert delivery carries different weight from campaign traffic, what data residency and audit expectations actually require, how each model meets a delivery commitment, what continuity looks like in each, and the hybrid arrangement that often satisfies both.
Why does an on-premise SMS server versus cloud choice carry different weight for bank alerts?
Because the message may become evidence.
A transaction alert is part of a service the customer paid for, and its absence can be disputed, so the ability to show what was sent and when matters as much as the delivery itself.
That changes the requirements in three ways. The record has to be complete enough to answer a dispute months later. The message has to be delivered within a window that the customer notices, which makes latency part of the obligation rather than an optimisation. And the delivery path has to survive events that marketing traffic would simply retry through, because a customer who does not receive a fraud alert is a different kind of problem from a campaign that arrives late.
The technical path is the same one every messaging deployment uses, defined in ETSI TS 123 040, but the operational expectations around it are higher. Recognising that difference early is what prevents a bank alert deployment from being designed as a high-volume campaign with better branding.
Data residency and audit expectations
They constrain where the record lives and who can produce it.
Residency requirements limit which jurisdictions may hold customer data, and audit expectations require the institution to produce its own record of what it sent.
In a cloud model, message content, recipient numbers and delivery records sit with a provider whose systems may be in several jurisdictions, and the institution has to be able to explain that arrangement to its supervisor. In an on-premise model the record sits inside the institution’s own environment, which simplifies the residency question and moves the audit obligation inward. Neither model removes the obligation; they place it differently, and the guidance published by the European Data Protection Board alongside the regulation itself on EUR-Lex is the reference point where the processing is in scope of that framework.
The audit question is narrower than the compliance question and it is the one that decides architecture. When a supervisor or an internal auditor asks for the messages sent to a given customer in a given month, can the institution produce them from systems it controls? Where the answer depends on a provider’s reporting interface and its retention window, the institution’s evidence is only as durable as its contract.
| Requirement | Cloud model | On-premise model |
|---|---|---|
| Residency of records | Provider jurisdictions, per terms | Institution’s own environment |
| Audit production | Depends on provider reporting | From internal systems |
| Retention control | Per contract and provider policy | Per internal policy |
| Access requests | Requires provider cooperation | Answered internally |
| Deletion evidence | Provider confirmation | Institution’s own records |
How does each model meet a delivery commitment?
One relies on a provider; the other on its own estate.
A cloud provider offers capacity across routes and regions, while an on-premise estate offers direct control over the radio path and its pacing.
The cloud model’s advantage is that capacity is somebody else’s problem, and its constraint is that the institution does not control the route a given message takes. For an alert that must arrive quickly, that is usually acceptable, because a provider offering multiple routes is more resilient than a single institution’s estate. The on-premise model inverts the trade: the route is known and controllable, and every failure mode belongs to the institution.
Where the deployment carries both alerts and campaign traffic, the two should be separated operationally even if they share hardware. Alert traffic has a latency expectation that campaign traffic does not, and a queue shared between them means a campaign can delay an alert. Separating the paths, or at minimum reserving capacity for alerts, is a design decision rather than a tuning exercise.
Continuity: what fails, and what happens next
Continuity is measured from the customer’s side, not the system’s.
The question is how long a customer waits for an alert that should already have arrived, which includes detection, switching and the recovery of anything queued.
Three failure modes dominate in an on-premise estate: a device, a site, and the network path the SIMs depend on. Each requires its own redundancy, and the site failure is the one that is most often overlooked because a second unit in the same rack is mistaken for redundancy. Fault management concepts including thresholds and clearing conditions are organised in ITU-T M.3400, and they are a workable structure for deciding which failures have to be detected and how quickly.
In a cloud model, continuity depends on the provider’s own redundancy and on the institution’s ability to keep submitting during a provider incident. Where a single provider holds the whole path, the institution’s continuity is the provider’s availability, which is why alert deployments that must meet a commitment usually combine a provider path with an owned path rather than choosing one.
Whichever arrangement is chosen, the queue should live above the paths so that a failure leaves the work where a surviving path can collect it, and message expiry should be defined so that a queue does not fill with alerts that are no longer useful.
One habit makes the framework repeatable: record the answer to each item with the date it was checked and the person who checked it. Alert delivery requirements are revisited when products change, when supervisors ask new questions and when the market list expands, and a dated record turns each of those moments into a short review rather than a fresh project.
Evidence and retention obligations
The record is the deliverable, not a by-product.
An alert deployment has to be able to produce the message, its destination, its time and its outcome, for a period the institution defines and can defend.
That requirement is more demanding than it first appears, because the record has to survive the systems that created it. Device logs are usually short-lived, reporting interfaces have their own windows, and export files created for a quarterly review become shadow archives. The practical arrangement is a defined retention period per record type, an export that runs on a schedule into storage the institution controls, and a deletion process that actually deletes.
Access-control and audit objectives that support this kind of evidence are organised in NIST SP 800-53 Rev. 5, and record-keeping practice for operational logs is covered in NIST SP 800-92. The test the institution should be able to pass is simple: pick a customer and a month, and produce the messages.
Can a hybrid model satisfy both?
Usually, and it is the common arrangement.
An owned path carries the traffic that has to be provable and controlled, while a provider path carries overflow and geographic reach.
The hybrid works because the two requirements that drive the decision are different. Control of the record pushes toward ownership; breadth of reach and peak absorption push toward a provider. Running both with a queue above them allows each to do what it is better at, provided that the routing decision is explicit: which traffic goes where, under what conditions, and who decides when the balance changes.
The hybrid also has a failure mode worth naming. Two paths configured without a documented routing policy tend to converge on whichever is easiest to send through, and the institution discovers after an incident that the path it believed was primary had not been used for months. Documenting the routing policy and verifying periodically that it is being followed is the control that keeps the hybrid real.
A decision framework
The framework is built around what the institution has to be able to demonstrate rather than around cost per message. Each question produces a requirement that can be checked against evidence, and the answers together describe which model, or which combination, satisfies the obligation.
- Which record must the institution be able to produce, for how long, and from where?
- What residency constraints apply to the markets served, and do they permit the provider’s jurisdictions?
- What delivery window does the alert commitment imply, and how is that measured rather than assumed?
- Which failure modes are in scope, and what redundancy does the availability target require for each?
- Is a provider path acceptable as part of the design, and if so for which traffic?
- Who owns the routing policy between paths, and how often is it verified?
The framework does not produce a preference; it produces a documented position. Where the answer is a hybrid, the position should say so explicitly, including which traffic uses which path, because that document is what the deployment will be judged against when something goes wrong.
One further step makes the position durable: assign an owner and a review date to it. Alert delivery requirements change as products change and as supervisors ask new questions, and a framework that was correct at commissioning becomes a description of history within a year. Reviewing it against the current product set is cheaper than discovering the gap during an audit, and the review is the point at which the hybrid routing policy is checked as well.
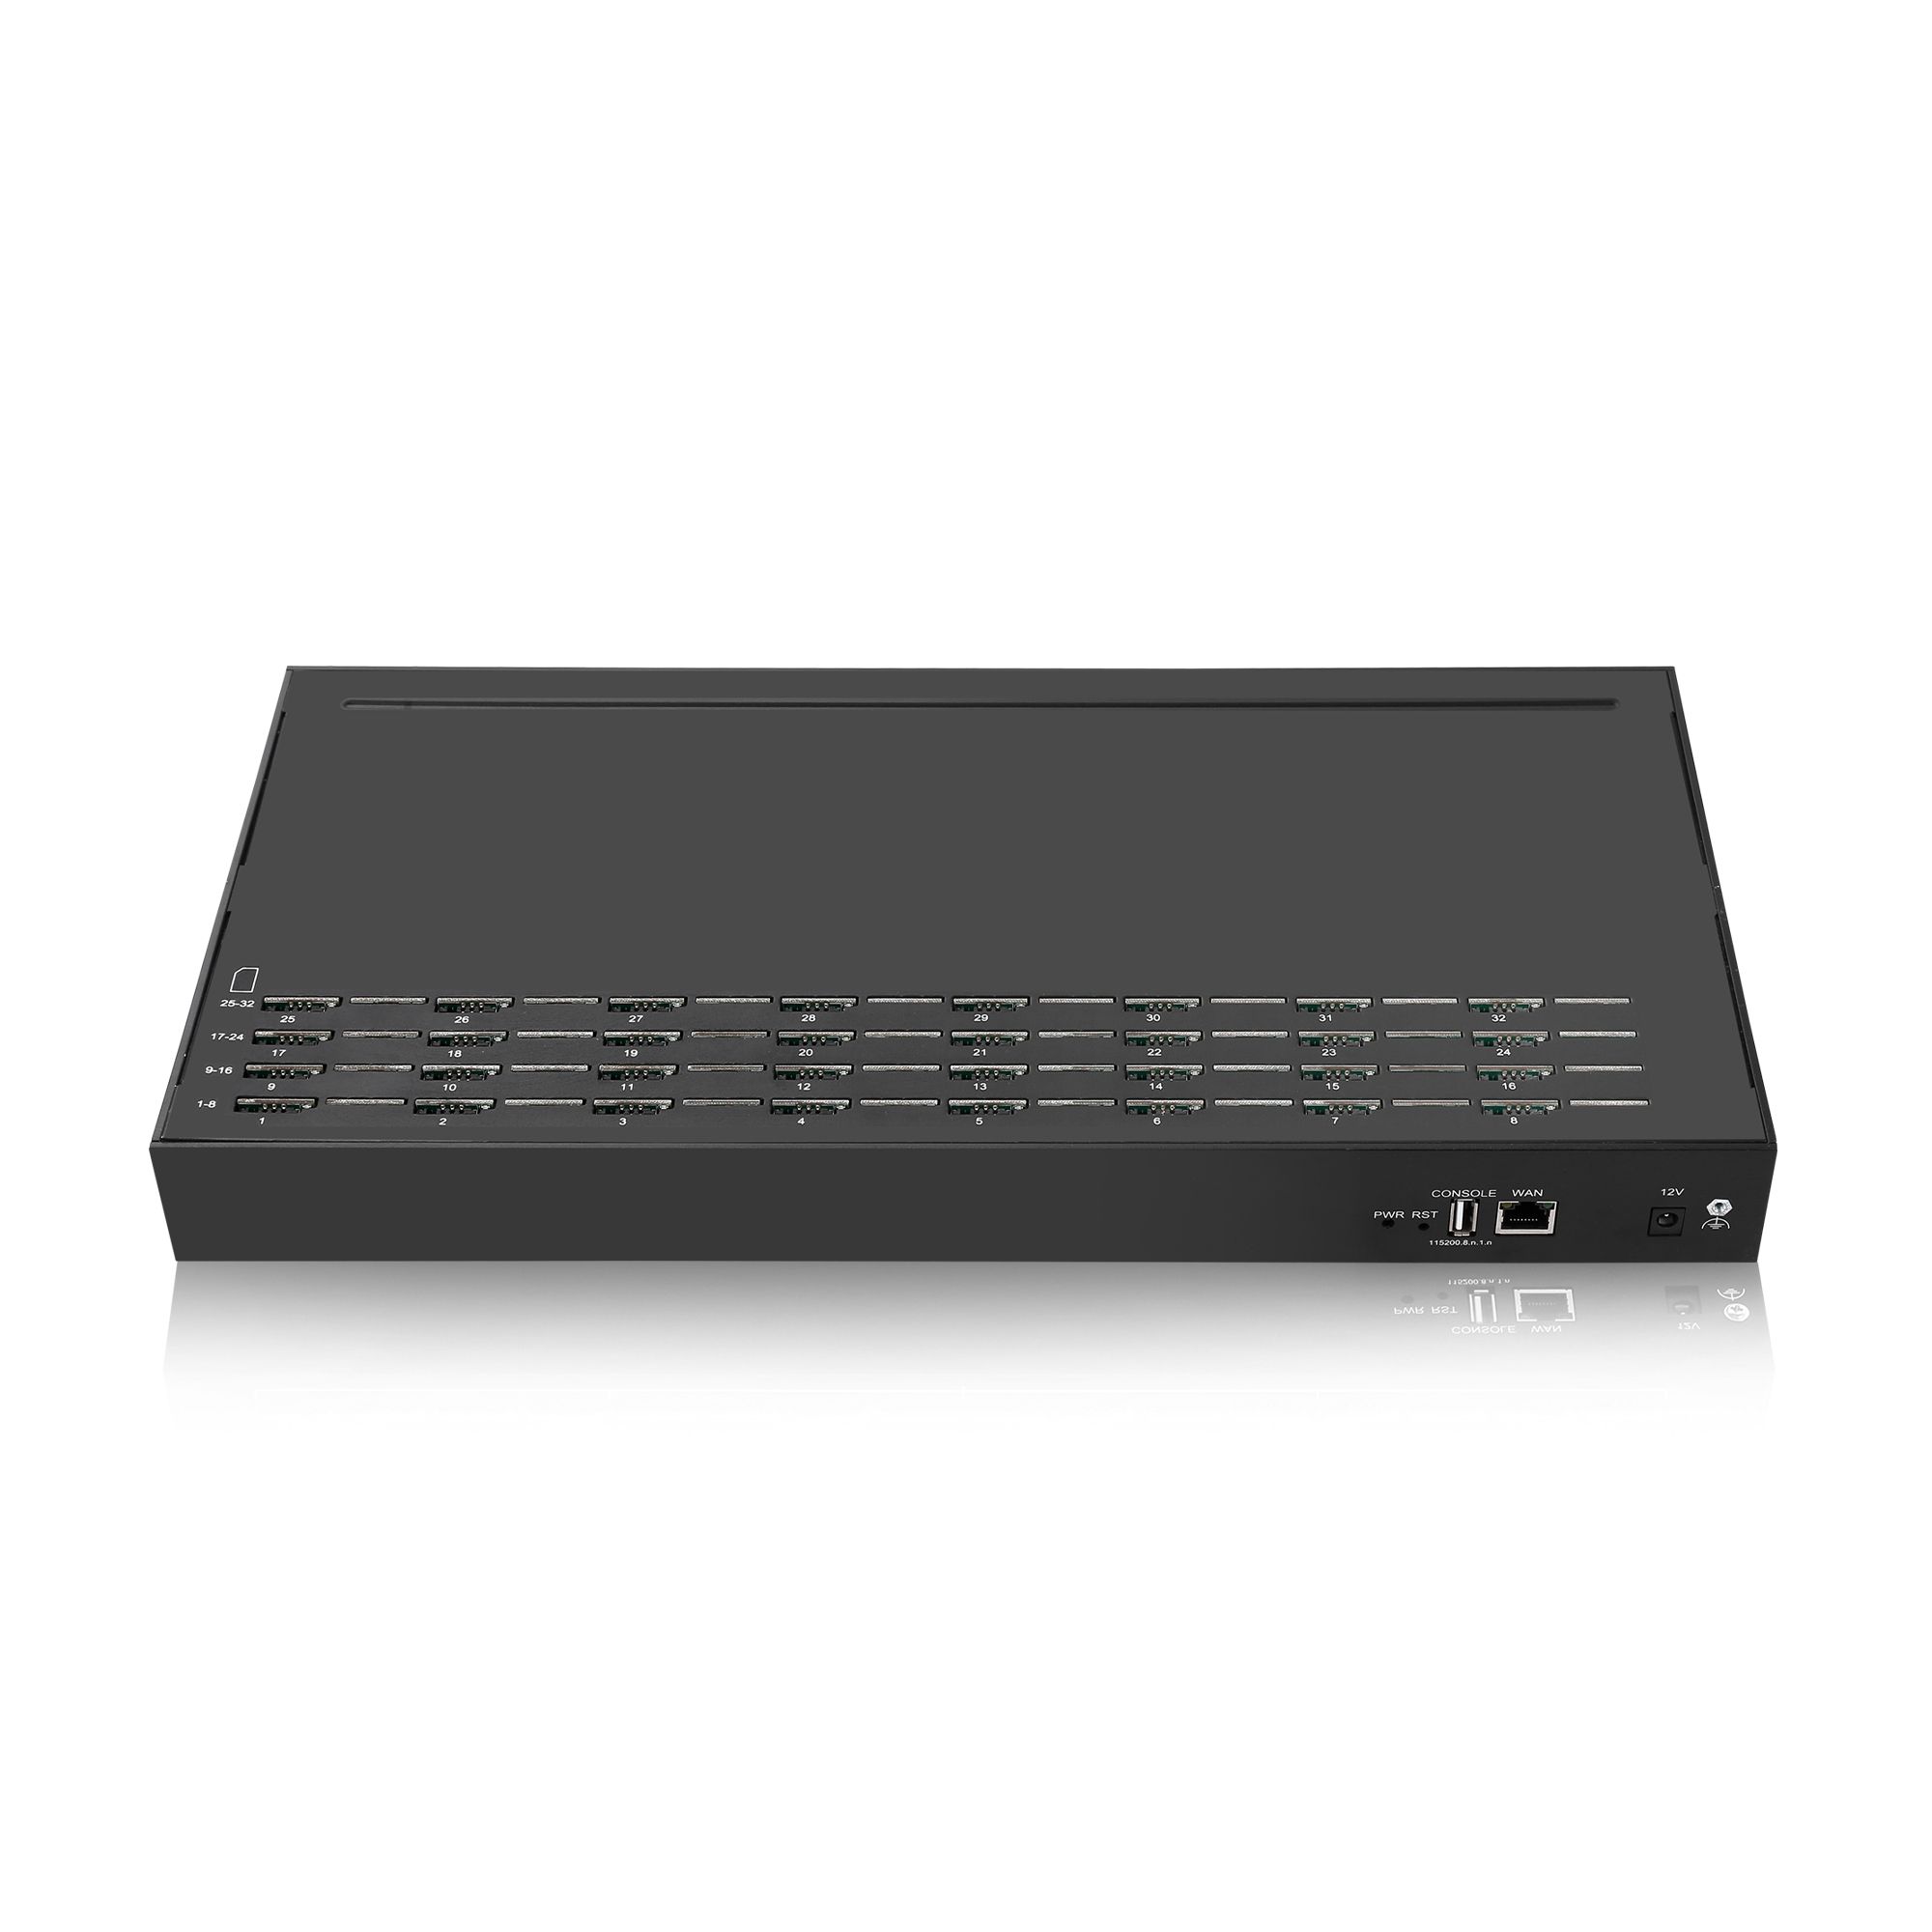
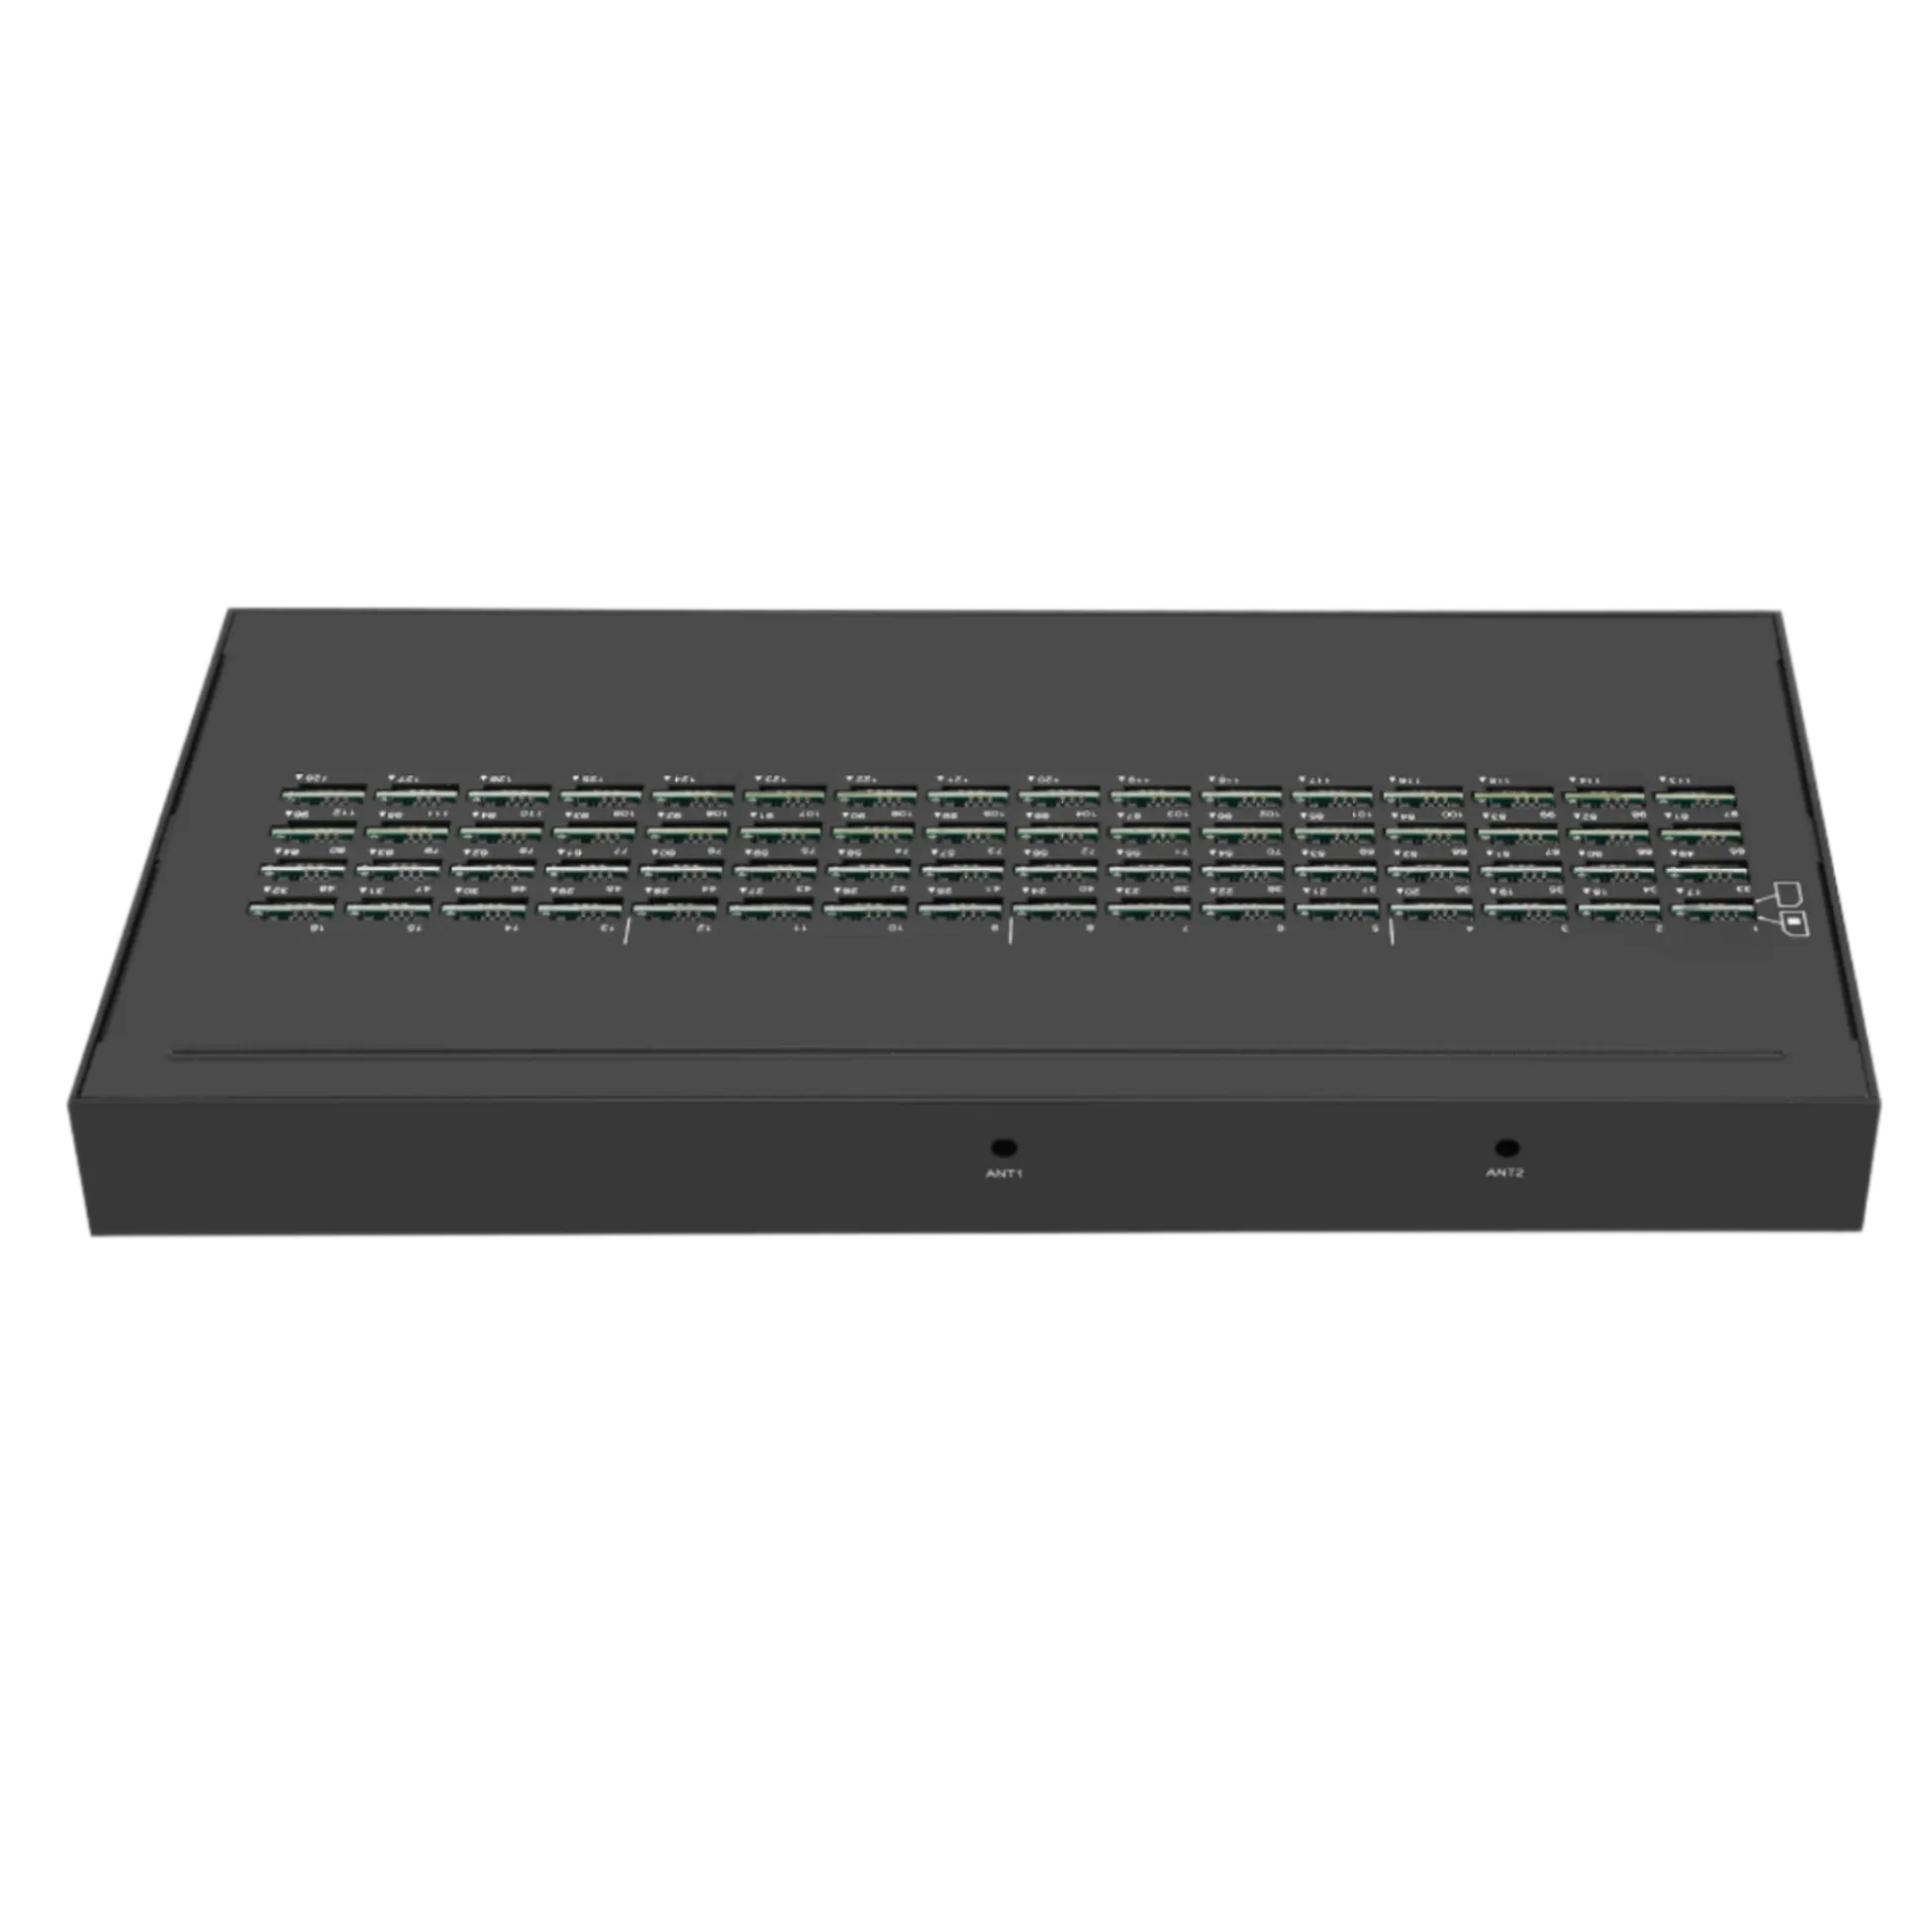
Start from the record you must be able to produce. Send your retention requirements, delivery window and market list to service@telarvo.com, or review the published configurations on the SMS gateway solution page and the SK-SMS Gateway range. Telarvo publishes the SIMBANK and SIMPOOL ranges on its product pages, and the configurations referenced above come from those listings.
FAQ
How much do banks charge for SMS alerts?
That is a commercial decision made by each institution and market, and there is no published figure to cite. It is also a different question from what the delivery costs: an institution that charges customers for alerts is pricing a service, while the infrastructure cost depends on whether it owns the path or buys capacity per message. Keep the two calculations separate.
Does on-premise equipment make alert delivery compliant?
No. It moves the processing into the institution environment, which can make the record easier to produce, but the obligations follow the data and the arrangement rather than the location of the hardware. Compliance is established by handling the data correctly, wherever it sits. Locality changes how easily a control can be demonstrated, not whether it is required. Record the flow, the roles and the retention window in one document so the position can be reviewed as a whole.
Can cloud delivery meet a strict alert window?
It can, provided the provider routes and the institution submission path are both measurable. The constraint is not the model but the visibility: an institution that cannot measure the end-to-end time has no way to demonstrate that it meets the window, whichever model it uses. Measurement is what turns a delivery commitment into a claim that can be evidenced. Measure the end-to-end time from the institution side as well, because that is the figure the commitment names.
What belongs in the routing policy for a hybrid arrangement?
Which traffic uses which path, the conditions under which traffic moves between them, who decides when the balance changes, and how the policy is verified. The verification matters most: without it, a hybrid drifts onto one path and the institution loses the redundancy it believed it had. A test that forces the switch is the only proof the second path works.
{
“@context”: “https://schema.org”,
“@type”: “FAQPage”,
“mainEntity”: [
{
“@type”: “Question”,
“name”: “How much do banks charge for SMS alerts?”,
“acceptedAnswer”: {
“@type”: “Answer”,
“text”: “That is a commercial decision made by each institution and market, and there is no published figure to cite. It is also a different question from what the delivery costs: an institution that charges customers for alerts is pricing a service, while the infrastructure cost depends on whether it owns the path or buys capacity per message. Keep the two calculations separate.”
}
},
{
“@type”: “Question”,
“name”: “Does on-premise equipment make alert delivery compliant?”,
“acceptedAnswer”: {
“@type”: “Answer”,
“text”: “No. It moves the processing into the institution environment, which can make the record easier to produce, but the obligations follow the data and the arrangement rather than the location of the hardware. Compliance is established by handling the data correctly, wherever it sits. Locality changes how easily a control can be demonstrated, not whether it is required. Record the flow, the roles and the retention window in one document so the position can be reviewed as a whole.”
}
},
{
“@type”: “Question”,
“name”: “Can cloud delivery meet a strict alert window?”,
“acceptedAnswer”: {
“@type”: “Answer”,
“text”: “It can, provided the provider routes and the institution submission path are both measurable. The constraint is not the model but the visibility: an institution that cannot measure the end-to-end time has no way to demonstrate that it meets the window, whichever model it uses. Measurement is what turns a delivery commitment into a claim that can be evidenced. Measure the end-to-end time from the institution side as well, because that is the figure the commitment names.”
}
},
{
“@type”: “Question”,
“name”: “What belongs in the routing policy for a hybrid arrangement?”,
“acceptedAnswer”: {
“@type”: “Answer”,
“text”: “Which traffic uses which path, the conditions under which traffic moves between them, who decides when the balance changes, and how the policy is verified. The verification matters most: without it, a hybrid drifts onto one path and the institution loses the redundancy it believed it had. A test that forces the switch is the only proof the second path works.”
}
}
]
}